The PHP Foundation has outlined how a major vulnerability that has sent the internet into a spin was discovered by AI and patched, as experts have warned that millions of attempts have already been made on the attack vector – and that some threat actors might even have been aware of the exploit before it was publicly disclosed.
Writing in a new blog post, the PHP Foundation said that it had released PHP versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35, all of which fix the critical bugs that lie at the core of this security incident.
The group also said that two related flaws lay at the heart of the matter. CVE-2026-109618 would allow remote code execution due to an out-of-memory corruption if triggered at exactly the wrong moment. CVE-2026-109619, meanwhile, involved an internal state pointing to memory that belonged to a past request, which would permit remote code execution as a result. Together, these bugs have become known as PHP2Shell.
Because these issues revolve around memory management and error handling, they “sit in parts of PHP that nearly every request touches,” the PHP Foundation said.
The group went on to disclose that “PHP Foundation found the first signs of the OOM problem behind CVE-2026-109618” during an audit in 2024, but since “no concrete vectors were found and other concrete issues with clear impact overshadowed these concerns,” little action was taken at the time.
And thanks to the potentially problematic consequences of the various proposed fixes – including backwards compatibility concerns, questions over compatibility with third-party extensions, and the potential for further attacks – work stalled for months. “The delay was a structural failure, caused by both the security team’s decision process and its lack of resources,” the PHP Foundation admitted, adding that it has since changed the way it works on security solutions.
The role of AI
Earlier this year, Alpha-Omega scanned PHP with Anthropic’s Claude Mythos, and PHP’s security team has since added OpenAI’s Daybreak Red to help validate vulnerability reports and exploits.
This year, PHP was added to OpenAI’s Patch the Planet program, which uses AI to find and fix software flaws. As part of that, security firm Calif began auditing PHP on July 30, 2026. On August 11, both Calif and OpenAI independently reported a similar out-of-memory bug to the one PHP had noticed in 2024.
Security company Wiz found another vector on August 24, and OpenAI added another on September 18. These reports made fixing the bug a priority from August 11 onwards.
An interesting wrinkle of the PHP saga is that it appears some threat actors knew about the flaw and were making active attempts to exploit it before it was publicly disclosed.
Cloudflare CEO Matthew Prince wrote on X that “In the 10 hours before it was publicly announced, across the Cloudflare network we saw thousands of attempts to exploit [the vulnerability]. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.”
Similarly, The Hacker News has reported that Amazon caught one attempt on October 17 – a full four days before the vulnerability was disclosed.
Part of that might be explained by the messy disclosure process. The flaws were intended to be announced on October 22 at 14:00 UTC, but it was found that the relevant CVE numbers were being discussed on forums as early as October 20. The PHP Foundation moved its disclosure date forward to October 21 in an attempt to compromise between acting quickly and ensuring fixes were available on time.
Calif then mistakenly published a video that showed the exploit in action and unveiled additional details about it. Although the video was deleted, it began circulating on social media. As well as that, mitigation advice given to critical infrastructure providers may also have leaked, while security firm Chainguard broke an embargo by publishing built images containing the fix more than six hours before the coordinated release.
This meant that “Any attacker could now study the fix in binary form while every other PHP user was still waiting for the release,” the PHP Foundation said.
Dan Lorenc, CEO of Chainguard, wrote on LinkedIn that he made the call to break the embargo after several other security vendors involved in the disclosure process confirmed seeing exploits in the wild.
That, combined with “how easily we were able to independently discover the vulnerability and build an exploit,” convinced Lorenc that disclosing the flaw and pushing out fixes ahead of schedule was the right call – something that the PHP Foundation evidently disagreed with.
Lorenc apologized for the added stress, saying the PHP Foundation and maintainers “did an amazing job here in a high stress situation.”
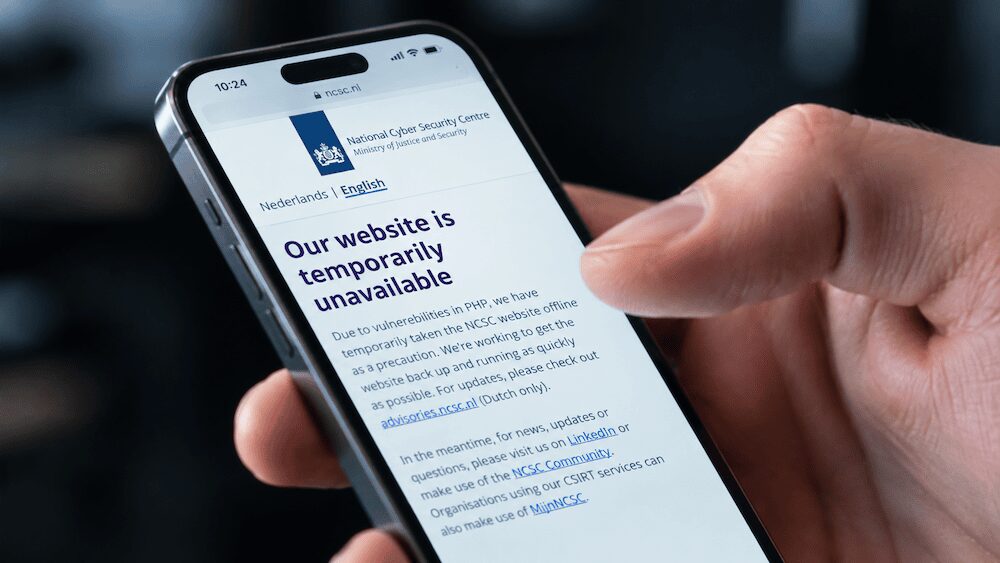
Dozens of high-profile websites across industry and government have been taken offline while they attempt to patch their PHP versions.
Now that the PHP Foundation has released several fixes, your organization should seek to patch its PHP operations as quickly as possible.